
Edr Deployment
EDR Deployment · To detect and respond to advanced threats...
Defence on Zero Day Room: Patch management, Multi-factor authentication and phishing resistance, Backup and recovery that survives ransomware, Network segmentation, Endpoint detection and response and Logging and detection engineering.
EDR Deployment · To detect and respond to advanced threats...

Data protection · Isolates data from network-based threats

Authentication security · Prevent credential theft and replay...

Control and monitoring of privileged... · Privileged session management, Privileged...
The Chinese-aligned EggStreme malware framework has been retooled with updated cryptography, a passive mode, and HTTP/3 to evade detection, targeting government entities in Southeast Asia.
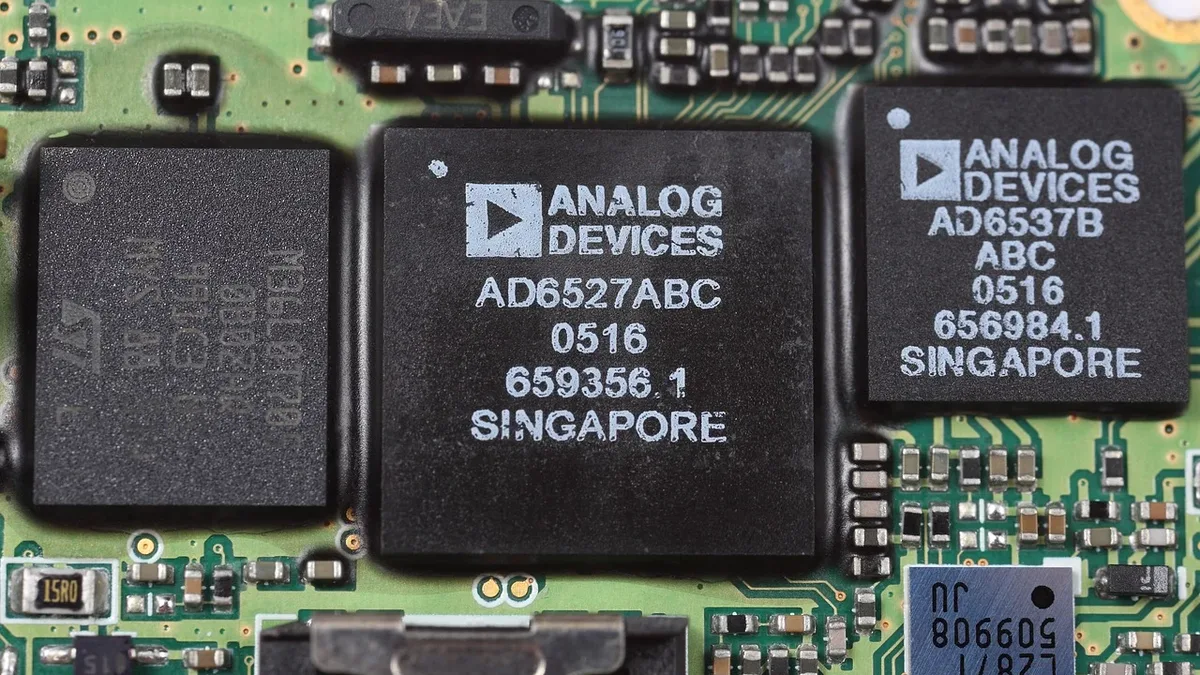
Trezor verified malicious hardware implants in three Safe 5 wallets sold by reseller CryptoBilis, designed to steal recovery phrases via cellular networks.
A security flaw in Claude Code's default configuration has exposed over 1,300 unique passwords and API keys across more than a thousand public GitHub repositories, with secrets persisting in git history and forks.
A ransomware attack on the Queens Public Library has caused a systemwide network outage, disabling on-site computers, Wi-Fi, and digital services while physical branches remain open.
Kaspersky researchers have uncovered NetamLoader, a new malware framework used in an attack on a custom Asian government Windows 10 build, employing advanced evasion and a multi-stage loading process.
ServiceNow introduced AI Passport, a cryptographic credential system for runtime governance of AI agents, alongside Shadow AI detection and AI Cost Management, with availability expected by year end and NVIDIA as a design partner.
The U.S. Treasury sanctioned 10 individuals and companies linked to a Tren de Aragua ATM malware scheme that caused over $40.7 million in losses.
A New Mexico jury found Meta's Facebook liable for over 43 million violations of state consumer protection law.
Kiteworks advised customers worldwide to shut down servers for a six-hour window on Saturday, September 26, based on credible threat intelligence.