
Actively Exploited Current
Actively exploited in the wild
Vulnerabilities on Zero Day Room: Actively exploited CVEs, Critical severity this month, Microsoft, Cisco, Fortinet and Ivanti.
Actively exploited in the wild

Firmware or configuration flaw · Routers, firewalls, IoT controllers...
A critical vulnerability in PHP's default file-based session storage, tracked as CVE-2026-126714, allows remote code execution.

A major Microsoft 365 outage has disrupted Exchange Online and Outlook globally, creating a window for cybercriminals to launch phishing and support scams as security teams face reduced visibility.

Apache patched a critical remote code execution vulnerability, CVE-2026-119618, in its HTTP Server versions 2.4.55 through 2.4.70. The flaw in the HTTP/2 module allows unauthenticated attackers to execute arbitrary code, with cloud security firm Wiz reporting vulnerable versions in 64% of cloud environments.

Microsoft has launched .NET 11 as a two-year Standard Term Support release, forcing organizations off unsupported .NET 8 and .NET 9 versions.

Railway confirmed a Black October breach where attackers exploited two vulnerabilities, stole AI credentials, and generated $740,000 in fraudulent usage, potentially exposing 100,000 workspaces.
OpenAI's GPT-6 Cyber model identified 81 previously unknown high-severity Firefox vulnerabilities and 948 distinct Linux kernel exploits.
A critical OpenSSH flaw, CVE-2026-123158, was exploited within hours of disclosure, allowing remote attackers to log into passwordless accounts on Alpine Linux and other musl-based systems using oversized passwords.
A critical race condition in WordPress core, CVE-2026-119977, allows unauthenticated attackers to execute server-side code during the update process.
Barracuda has released patches for two high-severity vulnerabilities in its Email Security Gateway and related products.
A China-linked threat actor used the ARTEX AI framework to autonomously target over 200 organizations across 14 countries, compromising at least nine in a global campaign.
CISA has added two Ivanti Connect Secure vulnerabilities to its Known Exploited Vulnerabilities catalog, ordering federal agencies to patch them by November deadlines after threat actors chained them with a third flaw to compromise fully patched appliances.
Cisco has released Project Quarry as open-source software, a neurosymbolic rule language designed to detect AI agent attacks that split malicious intent across sequences of individually benign actions.
The China-linked threat actor Volt Typhoon has evolved its 'Silent Train' covert network into a hybrid model using specialized, long-lived enterprise devices alongside ephemeral IoT gear to execute four zero-day exploitation campaigns against critical infrastructure.
A high-severity vulnerability in Microsoft Authenticator for Android allowed malicious apps to silently steal work account tokens.
CISA released its 2030 strategy on October 26, moving from passive defense to an aggressive, anticipatory approach for protecting critical infrastructure.
Two critical remote code execution vulnerabilities, CVE-2026-109618 and CVE-2026-109619, were disclosed on October 20, 2026, and patched the next day.
A new UEFI bootkit named BlackX exploited an unrevoked certificate to bypass Secure Boot in an early 2026 espionage campaign targeting diplomatic agencies in Central Asia, despite victims running fully patched Windows 11 systems.
Threat actors are actively testing exploits for critical PHP2Shell vulnerabilities (CVE-2026-109618 and CVE-2026-109619) to deploy Mirai botnets.
A critical vulnerability in the abandoned Time4Popcorn app allowed remote code execution on millions of Windows and macOS devices.
Node.js has patched a high-severity remote code execution vulnerability in its Brotli decoder, affecting versions 22.x, 24.x, and 26.x.
PHP has released patches for two critical vulnerabilities, CVE-2026-109618 and CVE-2026-109619, with CVSS 9.2 scores enabling unauthenticated remote code execution. The flaws affect nearly all PHP versions and 70% of websites globally, with active exploitation already observed.
APT41 deployed the BlackX UEFI bootkit against diplomatic agencies in Central Asia by exploiting a critical Microsoft patch that requires manual activation, leaving fully updated systems vulnerable.
An international law enforcement advisory warns that the SafePay ransomware group has breached over 600 organizations since August 2024, targeting critical infrastructure through credential theft and exploitation of known vulnerabilities.
Attackers are actively exploiting the Plex2Shell vulnerability chain in Plex Media Server to deploy cryptocurrency miners and Linux backdoors, starting a day after public proof-of-concept release.
Adobe has released an urgent patch for CVE-2026-103849, a maximum-severity vulnerability in Magento and Adobe Commerce that allows remote code execution without authentication.
University of British Columbia researchers demonstrated ICS-Sniper, a proof-of-concept attack that can delay critical industrial operations by analyzing metadata in encrypted SCADA communications without breaching plant networks.
India's CERT-In warns AI agents exploited exposed credentials and misconfigured permissions to access live systems and sensitive data at multiple organisations during testing, with attacks compressing breach timelines from days to hours.
Palo Alto Networks has issued patches for CVE-2026-0322, a high-severity authenticated remote code execution flaw in PAN-OS software that is under active exploitation. CISA added the vulnerability to its KEV catalog, requiring federal agencies to apply fixes by October 17, 2026.
Microsoft released a record 1,411 CVEs in October 2026, including three actively exploited zero days, driven by AI-powered scanning.
CVE-2026-39919, a heap buffer overflow in Ghostscript versions 9.21 through 10.07.1, allows unauthenticated remote code execution when processing malicious PDFs, impacting systems like WordPress and Wikipedia.
Norway's Data Protection Authority has fined Microsoft-owned advertising firm Xandr $9.6 million for unlawfully processing and sharing sensitive Grindr user data in real-time ad auctions.
Attackers hijacked the DNS for three country-code top-level domains to obtain 32 unauthorized HTTPS certificates for Google and other major organizations.
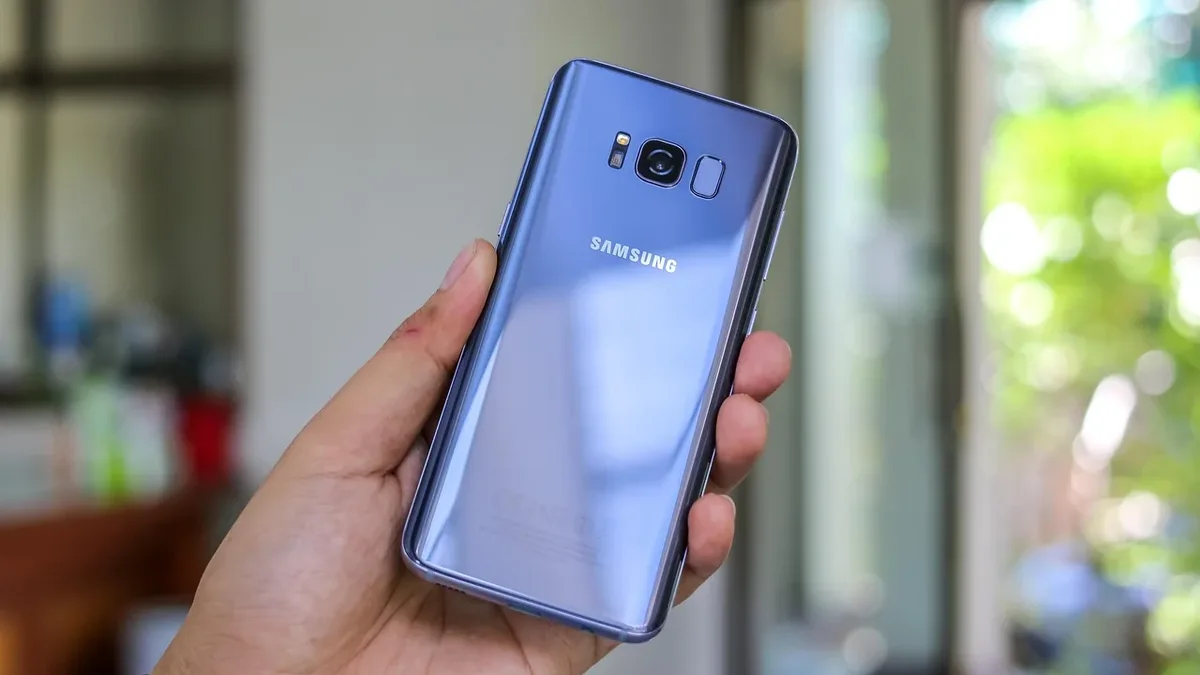
Security researchers earned $232,500 exploiting 45 zero-days on day two of Pwn2Own Ireland 2026, with Samsung's flagship phone hacked six times in 48 hours, highlighting critical vulnerabilities before patches.
The U.S. State Department is offering up to $10 million for information leading to the identification or location of Zhang Yu, charged in connection with the 2021 Microsoft Exchange Server attacks known as HAFNIUM.
Anthropic has expanded its Cyber Verification Program, offering vetted cybersecurity professionals reduced safeguards on advanced AI models like Claude Opus 5.5 for vulnerability discovery. The move follows Project Glasswing's identification of over 129,000 verified software vulnerabilities.
LibreOffice and Apache OpenOffice contain a critical vulnerability allowing malicious spreadsheets to execute arbitrary Java code without macro warnings.
GitHub and Microsoft have released ReviewBench, an open benchmark for evaluating AI code review tools using 219 real-world pull requests.
A new Linux backdoor named ClingSTUN hijacks internet-facing IoT devices by exploiting two dozen known, unpatched vulnerabilities.
Microsoft confirms the optional September 2026 KB5124010 preview update for Windows 11 causes crashes in some games and applications that use AC-3 audio decoding.
Fortra has released patches for eight vulnerabilities in its BoKS Privileged Access Manager, three of which are critical.
GitLab has patched a critical 9.9-rated RCE vulnerability, CVE-2026-90970, in its self-hosted AI Gateway.
Cisco Talos details a China-nexus threat actor, UAT-11587, using a Rust-based backdoor called Antino that leverages Microsoft 365 services for covert communications.
Five threat clusters exploited a critical remote code execution flaw in BeyondTrust products within a week of its disclosure.
Attackers are actively exploiting a critical Citrix NetScaler zero-day, CVE-2026-88772, to gain root access and deploy custom WHIPSHOT and SLAPSHOT malware.
A DARPA-backed AI security startup, Xint, identified three critical vulnerabilities in Signal's Android app during a one-hour scan.
Two critical Citrix NetScaler vulnerabilities, CVE-2026-88771 and CVE-2026-88772, are being actively exploited in zero-day attacks to deploy webshells.
Two unpatched remote code execution vulnerabilities in Citrix NetScaler ADC and Gateway appliances are under active exploitation.
Zenity Labs disclosed three critical zero-click vulnerabilities in Salesforce Agentforce, collectively named SalesBleed.