Danfoss Refrigeration Controller Cyberattack Hits French Supermarkets
A cyberattack on October 11 compromised legacy Danfoss refrigeration controllers, raising temperatures to 50°C in hundreds of French supermarkets and forcing massive food spoilage.
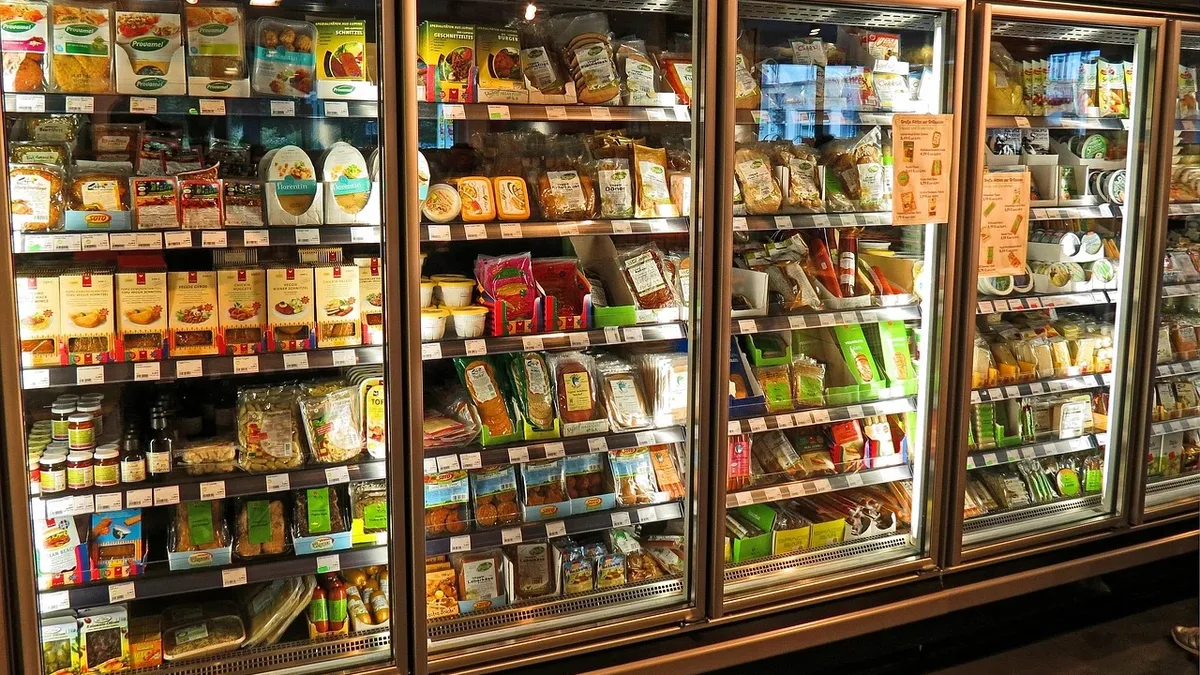
A cyberattack compromised refrigeration controllers in hundreds of French supermarkets, raising temperatures to 50°C and causing widespread food spoilage. Attackers took remote control of fridges and freezers on the night of October 11 and warmed them to as much as 50°C, forcing stores to discard food. The attack occurred overnight into Monday, with French television reporting attackers remotely triggered forced defrosting across numerous stores.
Affected supermarket chains include Intermarché, Netto, Coopérative U, E.Leclerc, and Carrefour. Les Mousquetaires, which owns the Intermarché chain, said fridges in about 150 of its stores reached 50°C for six hours. Retailers reported a wider tally of 300 or more Intermarché and Netto shops affected. Over 100 Coopérative U outlets were hit, and Carrefour said 80 of its supermarkets were attacked, though the vast majority of its 6,000 stores were not. Intermarché told affected branches to discard all fresh and frozen products. E.Leclerc said the attack hit one of its refrigeration equipment suppliers, disrupting cooling in several stores. Coopérative U chief executive Dominique Schelcher called the attack on food refrigeration equipment extremely serious and unprecedented.
Vulnerable legacy systems targeted
Attackers exploited outdated Danfoss controllers that no longer receive security updates, with some current models also affected due to outdated firmware. Danfoss characterized most affected hardware as legacy products which no longer receive software or security updates. It named two older models: the AK-SM 800 and the AK-SC 355. Danfoss declared the AK-SM 800 end-of-life in May 2021 and phased out the AK-SC 355 in 2016. Some units of the current model, the AK-SM 800A, were also hit. Those were running outdated firmware. Danfoss said it has long urged supermarkets to replace these legacy models.
French authorities identified a vulnerability in software supplied by a Danish company and contacted the vendor. CERT-FR, the French government's computer emergency response team, said it is aware of numerous compromises affecting two Danfoss controller series, the AK-SM and the AK-SC. Neither French authorities nor Danfoss has so far said who carried out the attack or how the attackers got into the controllers. As of October 13, CERT-FR had named no specific vulnerability and its alert warns against exposing management interfaces to the internet.
Official response and mitigation guidance
French cybersecurity agencies issued urgent alerts to disconnect or restrict access to affected controllers. ANSSI's head, Vincent Strubel, called it urgent to take the two series off the internet or filter access very tightly. CERT-FR's first instruction covers every AK-SM and AK-SC controller: disconnect it or filter access to it. Where remote administration cannot be avoided, limiting access to trusted IP addresses is a first, temporary step. The alert advises following CERT-FR's hardening recommendations.
Where a controller may have been compromised, the alert lists six steps: limit network access, perform a factory reset, apply all available security fixes, change the device's secrets, check existing accounts, and reconfigure the device completely. Danfoss told customers it was working on firmware updates where available, stronger network protections and removing direct internet exposure where applicable. Its general security guidance tells operators to keep controllers unreachable from the internet, change default passwords, and require remote logins through a single managed entry point.
The Paris prosecutor's office has opened an inquiry, led by its cybercrime section, to count victims and establish the link between the attack and reported damage. ANSSI is in contact with cybersecurity agencies in other European countries because those countries may be affected. A senior threat intelligence analyst said that Spain, Portugal, Poland, Germany and Belgium had also been affected.
Long-standing warnings unheeded
Danfoss had repeatedly advised customers to update firmware and replace legacy systems, but many units remained exposed and unpatched prior to the attack. The company said it had long advised customers to keep supported systems updated with the latest firmware and to migrate legacy systems to current-generation solutions. In an October 2025 newsletter, it said it would end all services for such older products and urged customers to plan replacements.
Software updates from Danfoss had previously fixed flaws allowing authentication bypass and code execution in newer models. Researchers at Claroty described three flaws in the AK-SM 800A in August, reporting they found thousands of its management interfaces reachable from the internet. Danfoss's own records show earlier attacks on the AK-SM 800: 16 Russian supermarkets were targeted in 2022, and 40 Israeli stores were hacked the same year.
Retailers are assessing financial losses from spoiled goods and equipment damage. Thierry Cotillard, who heads Les Mousquetaires, said he expected losses of tens of millions of euros across France.