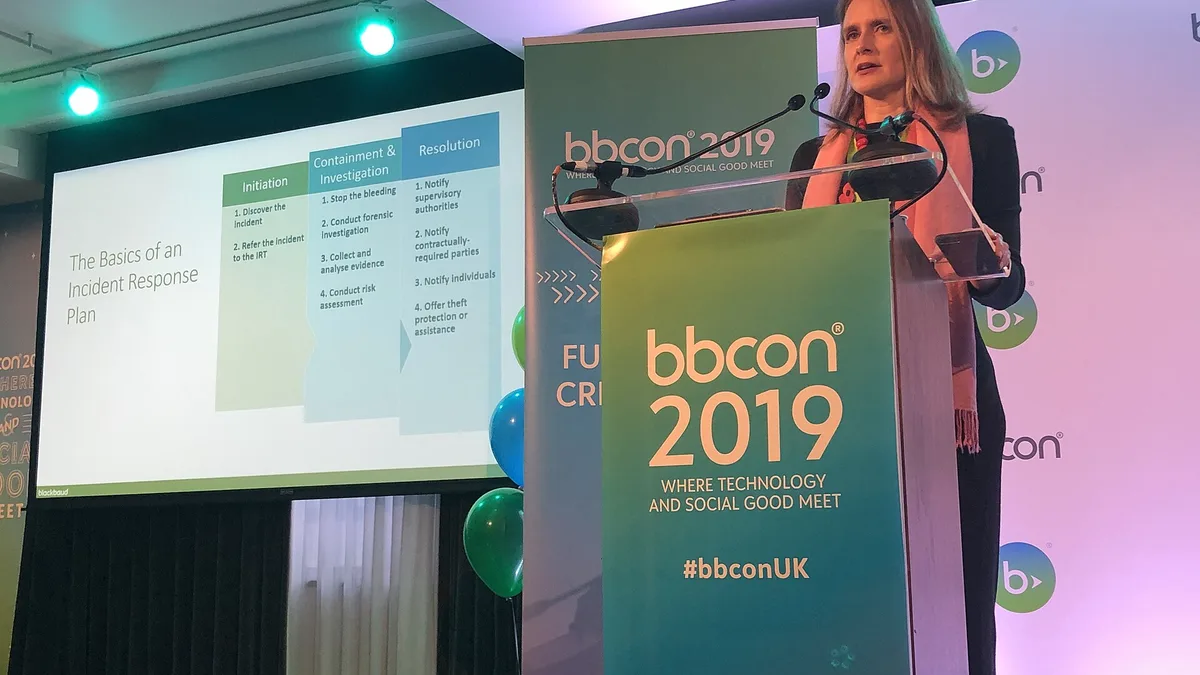
Incident Response Planning
| Vulnerability type | Process failure |
|---|---|
| Primary control | Formal documented plan |
| Core purpose | To contain and recover from a security breach |
| Key components | Roles, communications, procedures, recovery steps |
| Testing method | Tabletop exercises and simulations |
| Common failure | Plan exists but is not exercised or maintained |
| Related standard | ISO/IEC 27035 (Information security incident management) |
Origin and history
The formal discipline of Incident Response Planning originates from the United States in the late 20th century, driven by the increasing dependence on computer systems in government and business. Its development is closely tied to the establishment of the first Computer Emergency Response Team (CERT) at the Software Engineering Institute of Carnegie Mellon University in 1988, following the Morris Worm. Throughout the 1990s, as network connectivity expanded, the need for structured response moved from academic and military circles into the commercial sector. The creation of the National Institute of Standards and Technology (NIST) Special Publication 800-61 in the early 2000s provided a widely adopted framework, formalizing the practice. This evolution was paralleled in other regions, with similar teams and guidelines emerging in Europe and Asia, though the foundational methodologies are largely credited to U.S. initiatives. The practice has continuously evolved to address new threat landscapes, including advanced persistent threats and ransomware campaigns.
What it is for
Incident Response Planning is for establishing a predefined, organized approach for handling and managing the aftermath of a security breach or cyber attack. Its primary purpose is to limit damage, reduce recovery time and costs, and mitigate exploited vulnerabilities to prevent future incidents. The plan coordinates actions across technical teams, legal counsel, communications, and management to ensure a unified response. It is designed to comply with regulatory requirements that mandate specific reporting timelines and procedures following a data breach. Furthermore, it serves to preserve forensic evidence for potential legal action or criminal prosecution against attackers. Ultimately, it is for maintaining or restoring business continuity and protecting organizational reputation during a disruptive security event.
Overview
An Incident Response Plan is a documented set of instructions and procedures for detecting, responding to, and recovering from network security incidents. It typically follows a lifecycle model, such as the NIST framework which includes the phases of Preparation, Detection and Analysis, Containment, Eradication and Recovery, and Post-Incident Activity. The plan designates a specific Incident Response Team with defined roles, responsibilities, and chains of command for decision-making during a crisis. It includes communication protocols for internal stakeholders, external customers, law enforcement, and regulatory bodies. Critical components also encompass criteria for declaring an incident, escalation paths, and detailed technical playbooks for common attack types. The document is a living artifact that must be tested through exercises like tabletop simulations and updated based on lessons learned from real events and evolving threats.
What to know
Know that having a plan is fundamentally different from being prepared; the plan itself is useless without regular training, testing, and resource allocation. It is crucial to understand that legal and regulatory obligations, which vary by industry and jurisdiction, must be explicitly integrated into the plan's notification and evidence handling procedures. You should know that the plan must cover not just technical containment but also public relations and customer communication strategies to manage reputational fallout. Recognize that the definition of an "incident" should be clearly scoped to include data exfiltration, ransomware, denial-of-service attacks, and insider threats, among others. Be aware that effective plans are integrated with broader organizational risk management and business continuity frameworks, not standalone technical documents. Finally, know that the post-incident review phase is non-negotiable, as it is the mechanism for improving security posture and the plan itself.
Common questions
A common question is whether an organization can simply adopt a generic template plan found online, to which the answer is no, as plans must be tailored to specific infrastructure, risks, and legal contexts. Organizations often ask who should be on the Incident Response Team, requiring a cross-functional group including IT, security, legal, HR, and executive leadership. Many inquire about the cost, which is highly variable but primarily involves dedicating personnel time for development, training, and simulation exercises rather than purchasing a product. A frequent question concerns when to involve law enforcement, a decision that depends on the nature of the incident, the potential for prosecution, and the need for forensic assistance. People commonly ask how often a plan should be tested, with a general guideline being at least annually or after any significant change to the IT environment. Finally, there is often confusion about the difference between an incident response plan and a disaster recovery plan, the latter focusing primarily on restoring IT infrastructure after an outage, while the former deals with malicious activity.
Pros and cons
A major pro of a well-executed Incident Response Plan is the significant reduction in downtime and financial loss by enabling a swift, coordinated reaction, thereby limiting the attacker's dwell time. It also provides clear legal defensibility by demonstrating due care and facilitating compliance with breach notification laws. A significant con is the substantial and ongoing investment in time and resources required to maintain plan relevance and team readiness, which organizations often underestimate. A common mistake is creating a beautifully formatted plan that sits on a shelf, never exercised, leading to chaotic and ineffective responses during an actual crisis. Organizations frequently regret choosing overly complex plans that are difficult to execute under stress, or plans that lack clear authority lines, causing decision paralysis. Furthermore, a rigid plan can be a con if it does not allow for flexibility and adaptation when facing a novel or sophisticated attack not covered in the playbooks.
Who it suits
Incident Response Planning suits any organization that relies on information systems and handles sensitive data, making it a non-negotiable practice for regulated industries like finance, healthcare, and government. It is particularly critical for large enterprises with complex infrastructures and high-value assets that are attractive targets for advanced threat actors. Small and medium-sized businesses also suit having a basic plan, as they are frequently targeted due to perceived weaker defenses and need a structured approach to survive an attack. Organizations with a mature security posture benefit most, as they have the foundational monitoring and detection capabilities that make executing a plan feasible. It suits proactive leadership teams that understand cybersecurity risk as a business risk and are willing to fund the necessary preparation. Conversely, it is poorly suited for organizations with no dedicated IT or security staff unless they outsource the function to a managed security service provider that can act as their response team.
Latest Incident Response Planning news
Latest reporting
EU Auditors Cite Information-Sharing Gaps in Cyber Response
The EU Court of Auditors warns that insufficient information exchange and undefined roles are hindering the bloc's ability to detect and respond to...
KTH Researchers Train Agent to Reset OT Systems Under Attack
Researchers at KTH Royal Institute of Technology have developed an autonomous intrusion response agent for industrial control systems.
Suspected Iranian Hackers Shut UK Power Plant for Four Days
A British power plant was offline for four days in July 2026 after a suspected Iranian cyberattack, according to The Telegraph and Help Net Security...