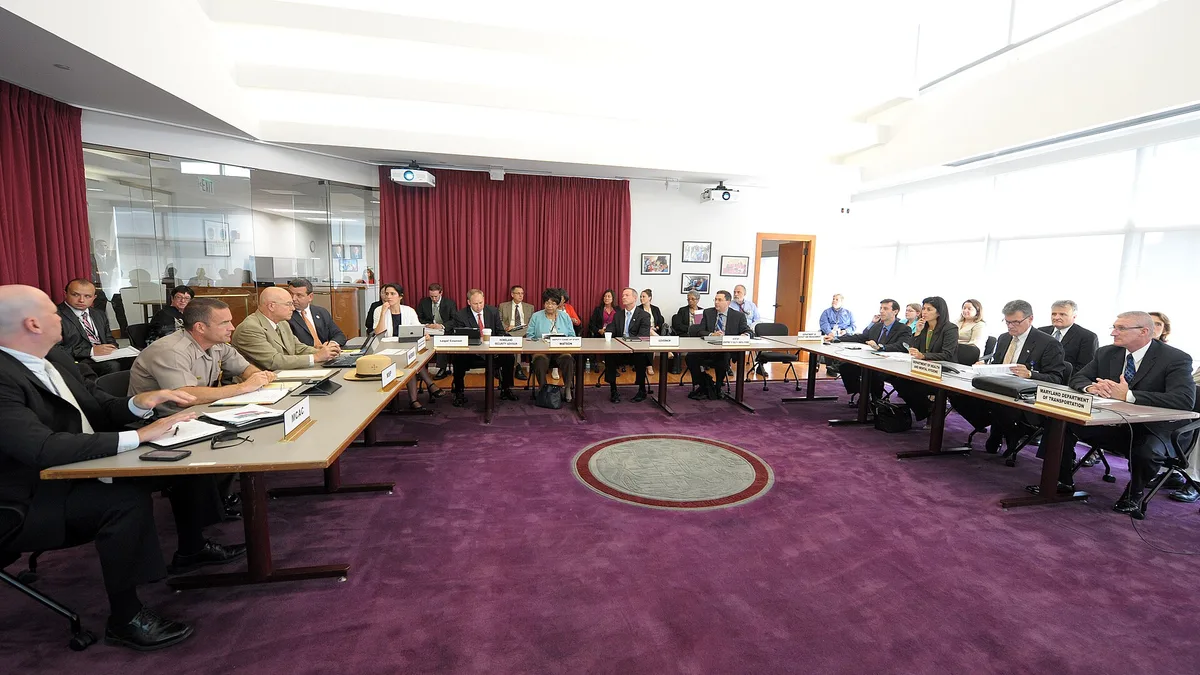
Tabletop Exercises
| Common name | Tabletop Exercises |
|---|---|
| Discipline | Cybersecurity, Emergency Management, Business Continuity |
| Original use | Training and preparedness evaluation |
| Participants | C-suite executives, IT staff, operational personnel, external stakeholders |
| Structure | Scenario-based, facilitated discussion |
| Typical duration | 2 to 8 hours |
| Primary deliverable | Identified gaps, actionable improvement plans |
| Vulnerability addressed | Organizational preparedness deficiencies |
Origin and history
Tabletop exercises originate from military and civil defense planning practices, with their use documented as early as the mid-20th century. They were formally adopted and structured within emergency management and business continuity disciplines in the latter decades of the 1900s. Their development is closely tied to Cold War-era preparedness drills in North America and Europe, designed to simulate response to crises without mobilizing physical resources. The methodology was subsequently adapted by the nuclear, aviation, and financial industries for risk management purposes. The formalization of tabletop exercises within cybersecurity incident response planning gained significant traction in the 1990s and 2000s. This adoption was driven by the increasing recognition that technical defenses alone were insufficient without trained personnel and tested processes.
What it is for
A tabletop exercise is primarily for testing and validating an organization's incident response plans, policies, and procedures in a low-stress, discussion-based environment. It serves to familiarize key personnel with their roles and responsibilities during a simulated crisis, such as a data breach or ransomware attack. The exercise is designed to surface gaps in communication channels, decision-making authority, and resource allocation before a real incident occurs. It functions as a training tool to improve team coordination and clarify escalation paths among technical staff, legal, communications, and executive management. Furthermore, it is used to assess the adequacy of existing security controls and identify procedural weaknesses that technical solutions cannot address. Ultimately, its purpose is to enhance organizational resilience by building muscle memory and reducing decision latency during actual emergencies.
Overview
A tabletop exercise is a facilitated, scenario-driven discussion where a team walks through their response to a simulated security incident. Participants gather in a room and are presented with a narrative of events, such as the discovery of a phishing campaign that led to a network compromise. The facilitator, often from a risk management or security team, injects new developments into the scenario to challenge the participants' plans. The discussion focuses on the "who, what, when, and how" of the response, examining steps like containment, eradication, recovery, and communication. Success is measured by the quality of discussion, the identification of process flaws, and the consensus on corrective actions, not by "solving" the scenario. The output is typically a formal report detailing lessons learned, assigned action items, and updates required for official response documentation.
What to know
Tabletop exercises are distinct from full-scale operational drills or technical penetration tests, as they focus on strategic and tactical decision-making rather than technical execution. Effective scenarios are plausible, relevant to the organization's threat landscape, and designed to test specific aspects of the response plan, such as external communications or legal compliance. The facilitator must be skilled in guiding conversation, managing dominant personalities, and ensuring all relevant departments contribute to the discussion. A common failure is involving only technical security staff; exercises must include representatives from legal, public relations, human resources, and senior leadership to be effective. The exercise should be conducted regularly, typically annually or biannually, to account for changes in staff, technology, and the threat environment. Critically, the value is lost if the identified action items from the after-action report are not tracked and implemented, rendering the exercise a mere theoretical discussion.
Common questions
A frequent question is how long a tabletop exercise should last, with typical sessions ranging from two to four hours to maintain engagement and focus. Organizations often ask what makes a good scenario, which is one that is credible, escalates in severity, and forces decisions with incomplete information. Many wonder who should participate, with the answer being a cross-functional team including incident responders, IT leadership, legal counsel, communications officers, and business unit representatives. A common concern is the cost, which is primarily the time of the participants and facilitator, as there is usually no need for expensive simulation technology. People ask how to measure success, which is based on the number of actionable findings and improvements to the plan, not on a score. Another recurring question is how to handle participants who treat it as a test of individual knowledge, which requires a facilitator to reinforce that the goal is to test the plan and processes, not the people.
Pros and cons
The primary advantage is the low-cost, low-risk revelation of critical flaws in response plans and team coordination that would only be discovered during a real, high-pressure incident. It builds relationships and a shared understanding of roles across disparate departments that may not interact daily. A significant pro is that it provides concrete evidence for audit and regulatory requirements concerning incident response preparedness. The most common con is the potential for the exercise to become a superficial, "check-the-box" activity if leadership does not champion it or follow up on findings. Participants often regret the time investment if the scenario is unrealistic, poorly facilitated, or results in no tangible changes to policies or resources. A frequent mistake is designing overly complex technical scenarios that sideline non-technical decision-makers, thereby missing the objective of testing organizational coordination.
Who it suits
Tabletop exercises suit any organization with a formalized incident response plan, regardless of size, as they are scalable in complexity and scope. They are particularly critical for organizations in heavily regulated industries like finance, healthcare, and energy, where response procedures are mandated. They are well-suited for senior management teams who need to understand the business impact of cyber incidents and their role in crisis management. Newly formed security or response teams benefit greatly from them as a mechanism to rapidly socialize and stress-test their initial plans. Organizations with a mature technical security posture but untested processes are ideal candidates, as the exercise shifts focus from prevention to response. Conversely, they are less suitable for organizations in extreme crisis or those with no foundational security policies, as the discussion will lack a framework to evaluate.