Trezor confirms hardware implants in three Safe 5 wallets
Trezor verified malicious hardware implants in three Safe 5 wallets sold by reseller CryptoBilis, designed to steal recovery phrases via cellular networks.
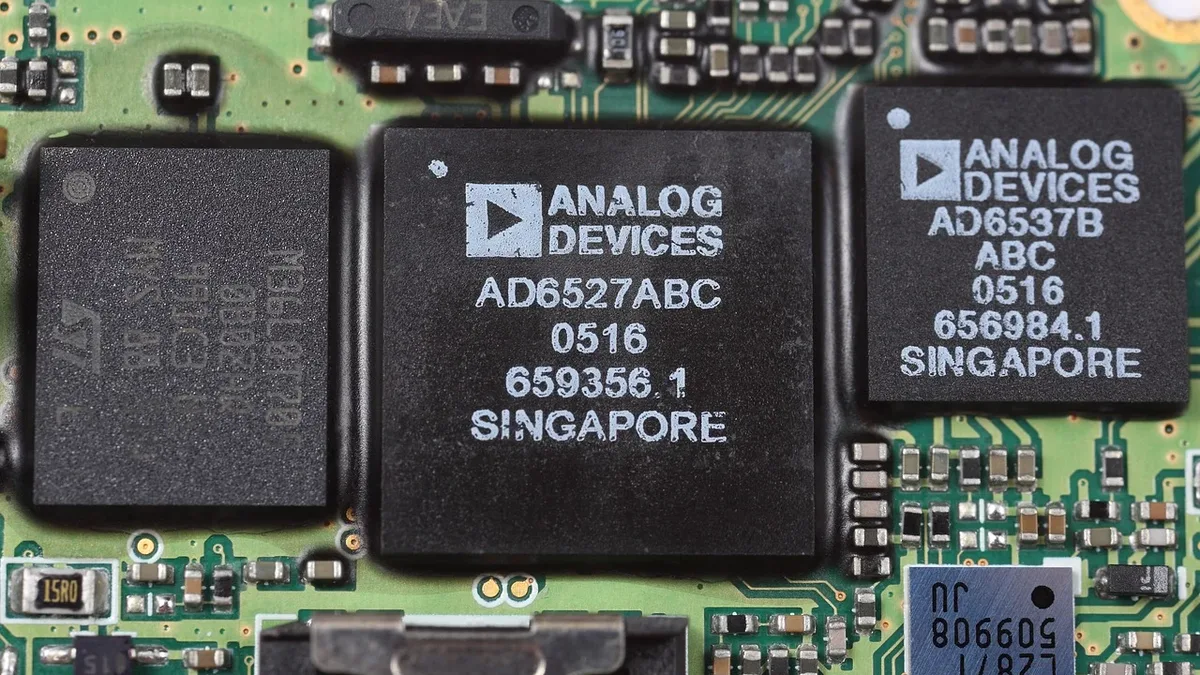
Trezor has confirmed malicious hardware implants in three of its Safe 5 wallets sold by the Southeast Asian reseller CryptoBilis. The implants were designed to steal wallet recovery phrases and transmit them to attackers over cellular networks. The three affected devices were purchased between August 20 and September 23, 2023.
Trezor released firmware version 2.13.1 on November 11, which includes protections that prevent the implants from capturing information on devices that run it. The update cannot protect wallet recovery phrases that may have already been captured before installation. Ledger also confirmed unauthorized implants in its wallets sold by CryptoBilis on October 9, 2023.
Implants captured recovery phrases without firmware changes
The implants consist of an additional circuit board installed between the Safe 5's main board and display. This allowed it to monitor screen activity without modifying the device's legitimate firmware or Secure Element. The implant collects wallet recovery words when they appear on the screen during wallet creation or restoration, and can also capture passphrases displayed on the screen.
Trezor warned of a suspected implant on October 30, two days after a buyer reported it. The company examined the original device in its laboratory and identified two additional compromised wallets using photographs submitted by their owners. The implants were limited to Safe 5 wallets sold through CryptoBilis.
Trezor firmware update mitigates new devices but not past thefts
The firmware update, version 2.13.1, is available for the Safe 7, Safe 5, Safe 3, and Model T. It stops the implants from capturing data on updated devices. Trezor will not ask for a recovery phrase and warns against scammers posing as Trezor offering replacements or refunds.
Forty-eight CryptoBilis customers contacted Trezor following its October warning, with devices being examined in its laboratory or through photographs of their internal components. None of the three owners of the confirmed compromised wallets reported lost funds. Trezor makes its wallets self-custodial and cannot see anyone's balance.
Supply-chain crackdown follows Ledger and CryptoBilis investigations
Trezor reduced its global reseller network by approximately 80% on October 13, 2023, due to supply-chain attacks. This followed reports of compromised Ledger wallets sold through CryptoBilis, before Trezor learned of implants in its own devices. CryptoBilis served as an official Trezor reseller in Southeast Asia until October 9, when Trezor removed it.
Trezor inspected devices from other resellers in the region and found no evidence of tampering. The company previously announced plans to reduce its reseller network in October. Dropped resellers may sell existing stock until January 1, 2027.
The implant encrypts stolen information and transmits it over a mobile network to an attacker-controlled server. It holds data if a connection is unavailable until transmission succeeds. Trezor advised customers who purchased devices from CryptoBilis since March 2023 to transfer cryptocurrency to a newly created wallet using a new recovery phrase. Trezor offered replacement devices to anyone who bought a Trezor wallet from CryptoBilis since that date. No affected customers have reported losing funds. Trezor instructed all buyers of Trezor wallets from CryptoBilis since March to move funds to new wallets with new recovery phrases.